Security
MCP server security, enforced on every query
MCP server security for a database comes down to four questions: can the agent write, what can it read, whose access is it using, and can you prove what happened. Datablare answers each one in code — read-only enforced twice, tables and columns you choose, per-person sign-in, and an audit log of every call.
Read-only database access for AI agents
Read-only, enforced twice
A single lock is one bug away from a bad day. Datablare puts two in front of your data: its own SQL guard, then the database itself.
- A normal question
SELECT name, total FROM orders …SQL guard: Passes: one SELECT Database: Runs read-only Rows returned - An agent tries to write
DELETE FROM orders WHERE …SQL guard: Refused: writes are not allowed Database: Never reached Never reaches your data - The belt-and-braces case
A write the guard missedSQL guard: Suppose it slips past Database: Refused by the database Nothing changes
Illustration of real behaviour. Every refusal is recorded in the audit log.
Lock 1: the SQL guard
Every statement is checked before it is sent: one statement, a read, no data-changing or schema-changing commands and no side-effect functions. Anything else is refused and recorded with the reason.
Lock 2: the database
PostgreSQL, MySQL, MariaDB, Oracle and ClickHouse run the query in a read-only session. SQL Server and Snowflake run it in a transaction that is always rolled back. Either way, a write that slipped past the guard would not land.
MCP access control
Only the tables and columns you allow, for the people you allow
The AI only sees the tables and columns you allow — enforced by Datablare, not by asking the model nicely.
-
Tables per project
Each project exposes only the tables you select. Everything else does not exist as far as the agent knows.
-
Hidden columns
Hide a column and it is refused in every query, even through SELECT *, an alias, a function or a subquery, and checked again on the result.
-
Roles and sources
Managers run the project, analysts query it, viewers see activity only. An analyst can be limited to specific data sources.
-
Per-person sign-in
People connect with OAuth as themselves. Every connection carries their name; remove someone and their connections stop at once.
MCP audit logging
Every query on record, with the question behind it
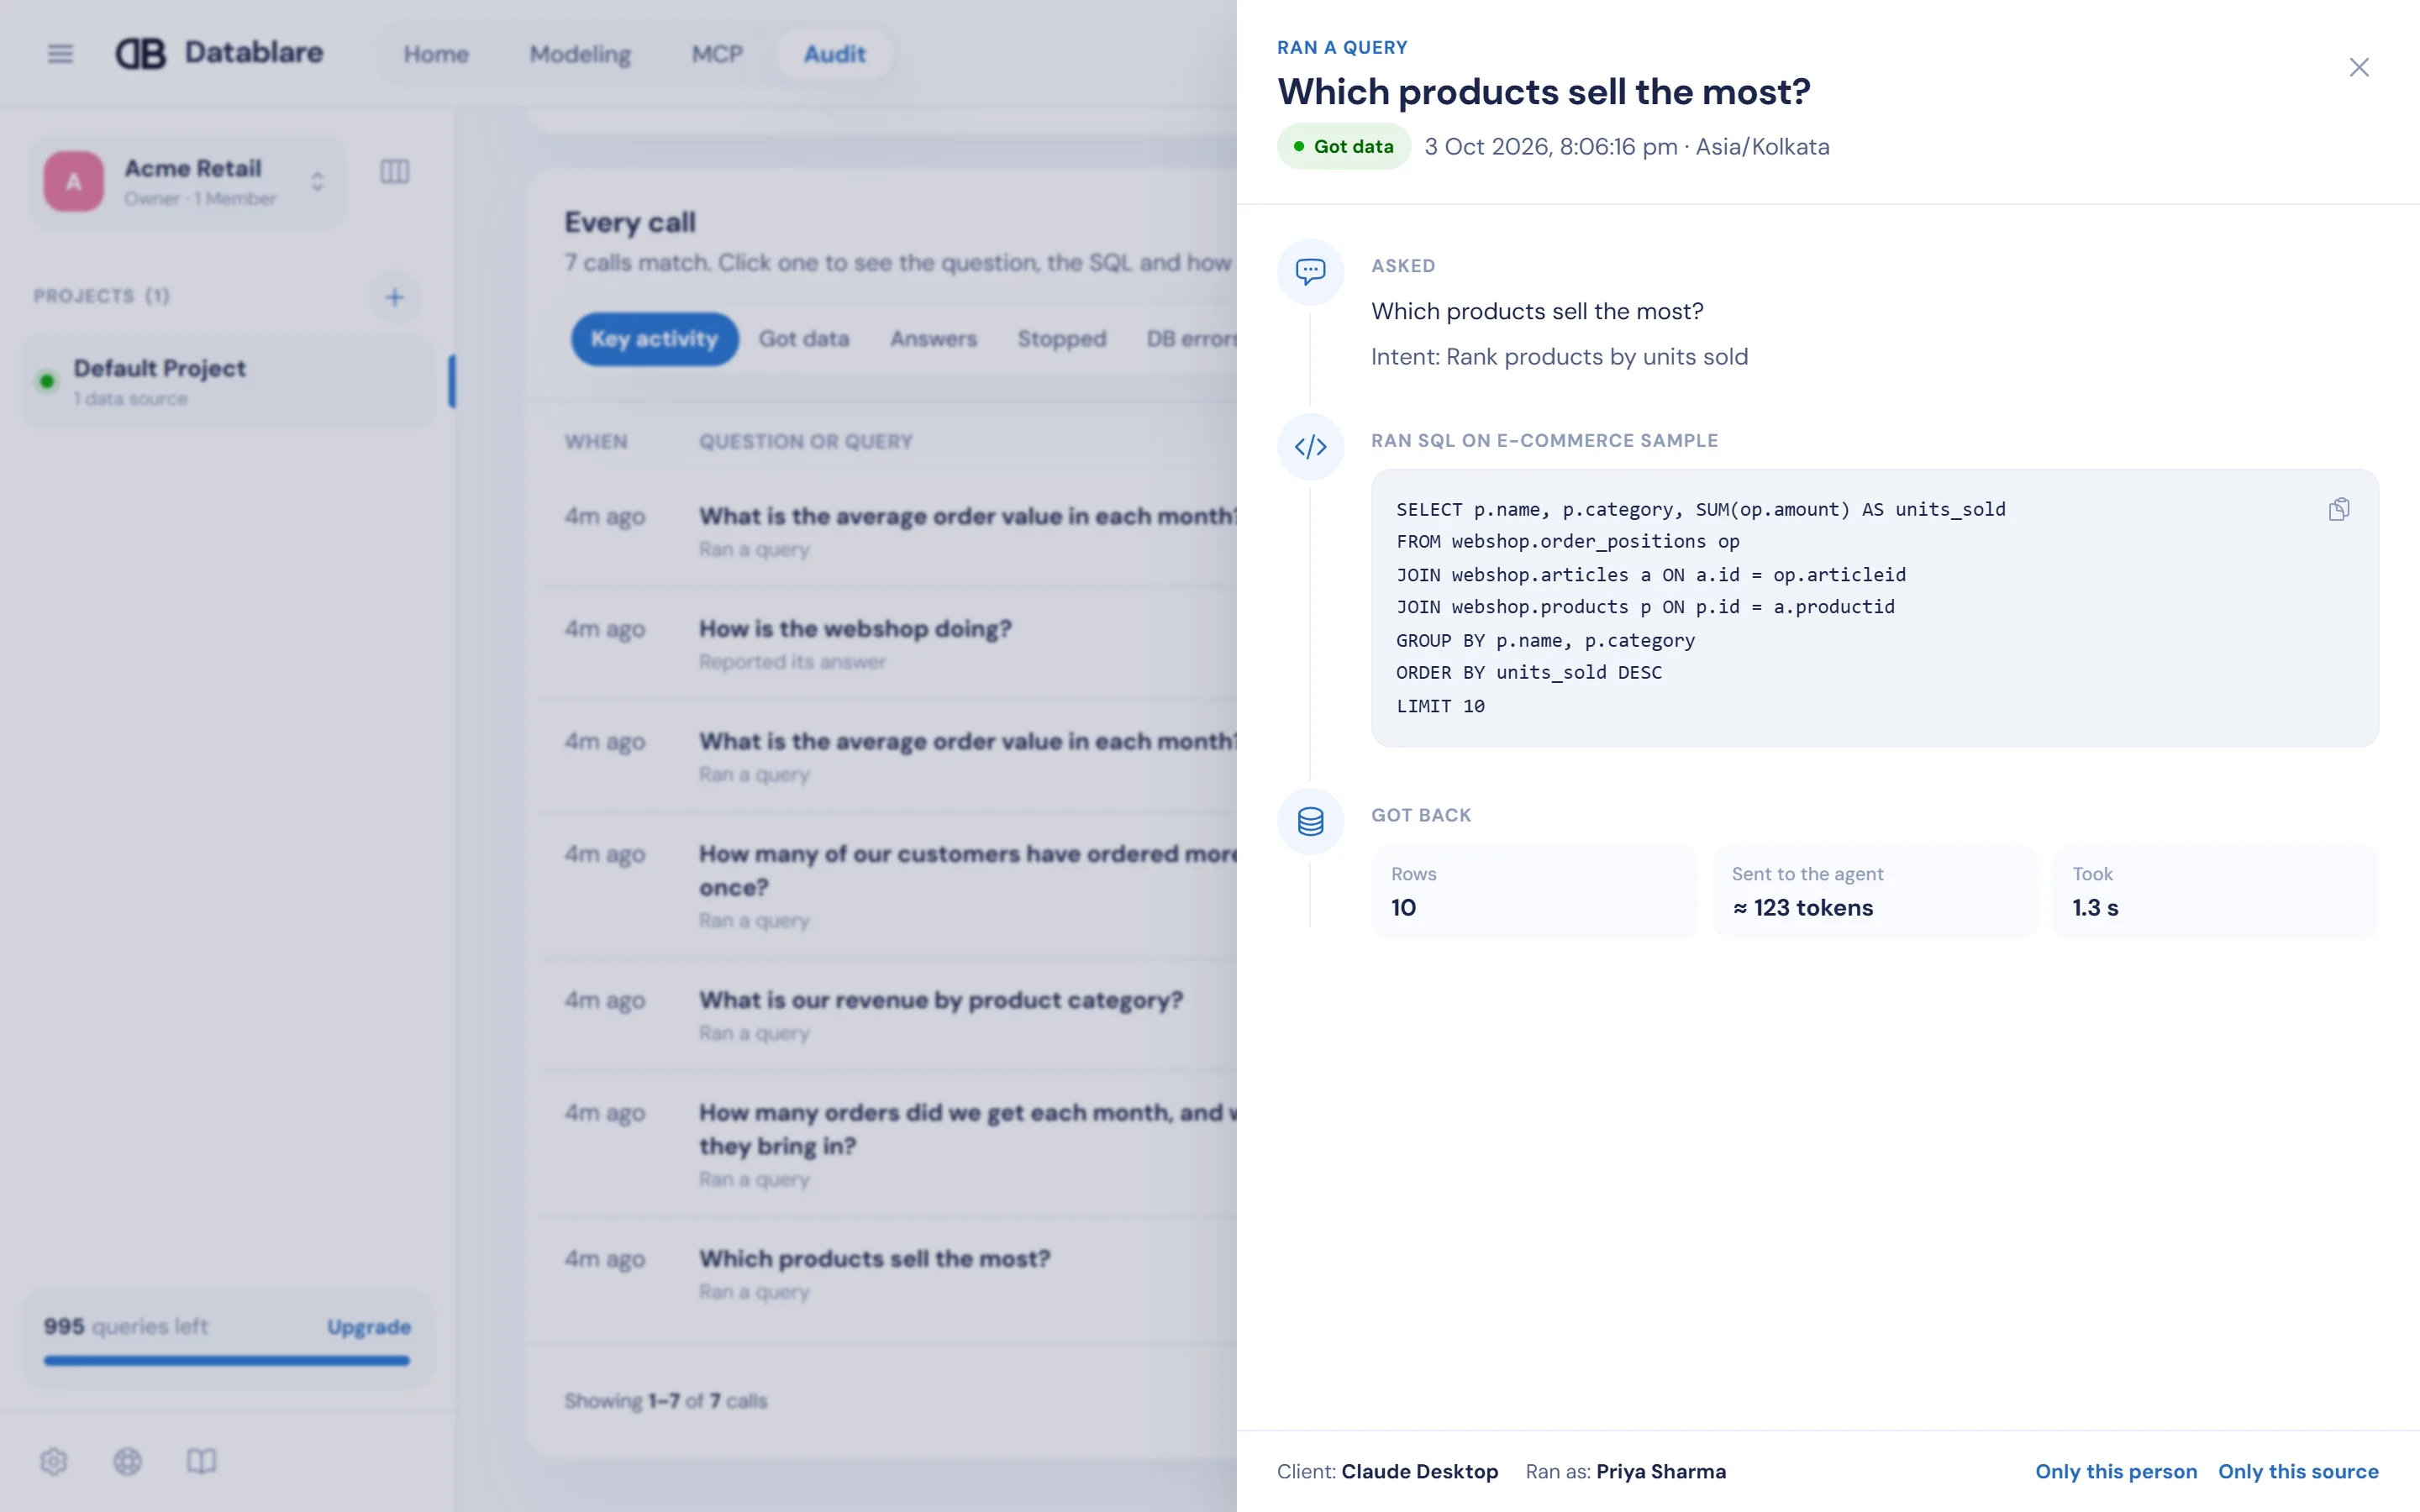
When someone asks “which customer data did AI tools read last month?”, open Audit. Each call shows who asked, from which client, the question, the SQL, the tables touched, rows returned and time taken — refusals included.
- Free
- 7 days
- Team
- 30 days
- Business
- Full history
Audit history kept per plan. CSV export on Team, Business and Enterprise.
Data handling
What Datablare keeps, and what it never does
-
Query results are never stored
Rows pass through to the AI tool and are not kept by Datablare. The audit log holds the question, SQL and timings, never the rows.
-
Credentials are encrypted
Database passwords and keys are encrypted at rest and never shown back, not even to admins.
-
Hosted in India
Datablare Cloud runs in India. Enterprise customers can talk to us about deploying in their own cloud.
-
Private databases
Reach a database that is not on the internet through an SSH tunnel to a bastion host you control.
-
Limits on every query
Row limits, statement timeouts and a result-size cap keep one question from straining your database.
-
Instant revocation
Revoke any key or connected app immediately. Signing out everywhere or resetting a password revokes them too.
The full list of what we store, for how long, and which processors we use is in the Privacy Policy.
DPDP AI governance
AI on customer data, the DPDP way
Under India’s DPDP Act your organization is the data fiduciary for the personal data in your databases, and Datablare acts as a data processor on your instructions. The controls above are what make AI access defensible: purpose-limited tables, hidden identity columns, India hosting and a record of every access.
Talk to a person
Security questionnaire, DPA question or an architecture review? Our Grievance Officer and founder, Kamal Thakur, answers directly.
Responsible disclosure
Report a security issue
If you think you have found a vulnerability in Datablare, please tell us privately first. We read every report and will acknowledge yours within 48 hours.
What to report
Anything on datablare.com, app.datablare.com or a project’s MCP link that could expose data or access: a way past the read-only guard or a hidden column, reaching another organization’s data, sign-in or OAuth flaws, or injection and cross-site scripting.
How to report
Email kamal@datablare.com or message WhatsApp +91-80912-50294 with the affected URL, the steps to reproduce and what an attacker could do. We acknowledge within 48 hours and keep you updated until it is fixed.
Please don’t
Access, change or delete other people’s data — test with your own account and the sample dataset. Don’t disrupt the service (no load or denial-of-service testing, spam or social engineering), and give us reasonable time to fix an issue before you share it.
Our contact details for researchers are also published at /.well-known/security.txt.
Built for regulated data
Helps you meet the privacy laws your customers ask about
Datablare gives you the controls auditors look for when AI tools touch personal data. Compliance stays yours; these make it much easier to show.
Helps you meet
- DPDP
- GDPR
- HIPAA
- CCPA/CPRA
- PDPL
-
Read-only
Enforced by the SQL guard and by the database itself.
-
Column-level control
Hide personal data columns from every agent.
-
Full audit trail
Who asked, the SQL, the tables touched, when.
-
Hosted in India
Or deployed in your own cloud for Enterprise.
FAQ
Security questions
What are the main MCP server security risks with databases?
An agent holding a login that can write, an agent that can read every table and column, prompts that trick an agent into running something it should not, and no record of what was read. Datablare addresses each: read-only enforced twice, tables and hidden columns per project, per-person access, and an audit log of every call.
How is read-only enforced?
Twice. Datablare’s SQL guard refuses anything that is not a single read. Then the database itself keeps the query read-only: a read-only session on PostgreSQL, MySQL, MariaDB, Oracle and ClickHouse, and a transaction that is always rolled back on SQL Server and Snowflake. We also recommend connecting with a read-only database login, which Datablare checks when you test the connection.
What exactly does the audit log record?
Who asked, which AI client and connection, the question, the SQL, the data source and tables touched, how many rows came back, how long it took, and whether it was refused and why. It never stores result rows. Audit history is kept 7 days on Free, 30 days on Team, and for the life of the organization on Business and Enterprise; paid plans can export it as CSV.
Does Datablare help with DPDP compliance?
It helps you meet your DPDP obligations when AI tools read personal data: limit access to what is needed, hide identity columns, keep data hosted in India, and show who accessed what. For data in your connected databases, your organization is the data fiduciary and Datablare acts as a data processor on your instructions.
Does Datablare hold a security certification?
Not today, and we do not claim one. We are happy to walk through how Datablare works, answer your security questionnaire and share what we can about our hosting and processes. Ask on WhatsApp or email.
Can a prompt injection make the agent leak hidden data?
A hidden column is enforced by Datablare, not by the prompt: a query that reads it is refused whatever the agent was told, and the result is checked again before it is returned. Tables outside the project are refused the same way.
See the audit log for yourself.
Connect the sample dataset, ask Claude a question, and open Audit. It takes about two minutes.
30 minutes with the founder. Or WhatsApp / kamal@datablare.com